STRATUM
STRATUM joins each runtime eBPF alert to the running image digest, the CI run and commit named by that digest's verified Sigstore certificate, and the Zero-Trust control that should have stopped it.
In 5 live kind + Tetragon jobs, each with its own signed image and Fulcio certificate, all 55 demo-pod alerts traced to the right commit (5 / 5 runs, Wilson 95% CI 0.57-1.00). An unsigned image carrying the right revision label traced to none; label provenance (arm A2) and a repository-level join (A4) attributed it to the commit in 5 / 5 runs, the digest-exact certificate join (A3) in 0 / 5 (results/live.md, run 37085766270).
Try it in 60 seconds How it works Evaluation Console demo
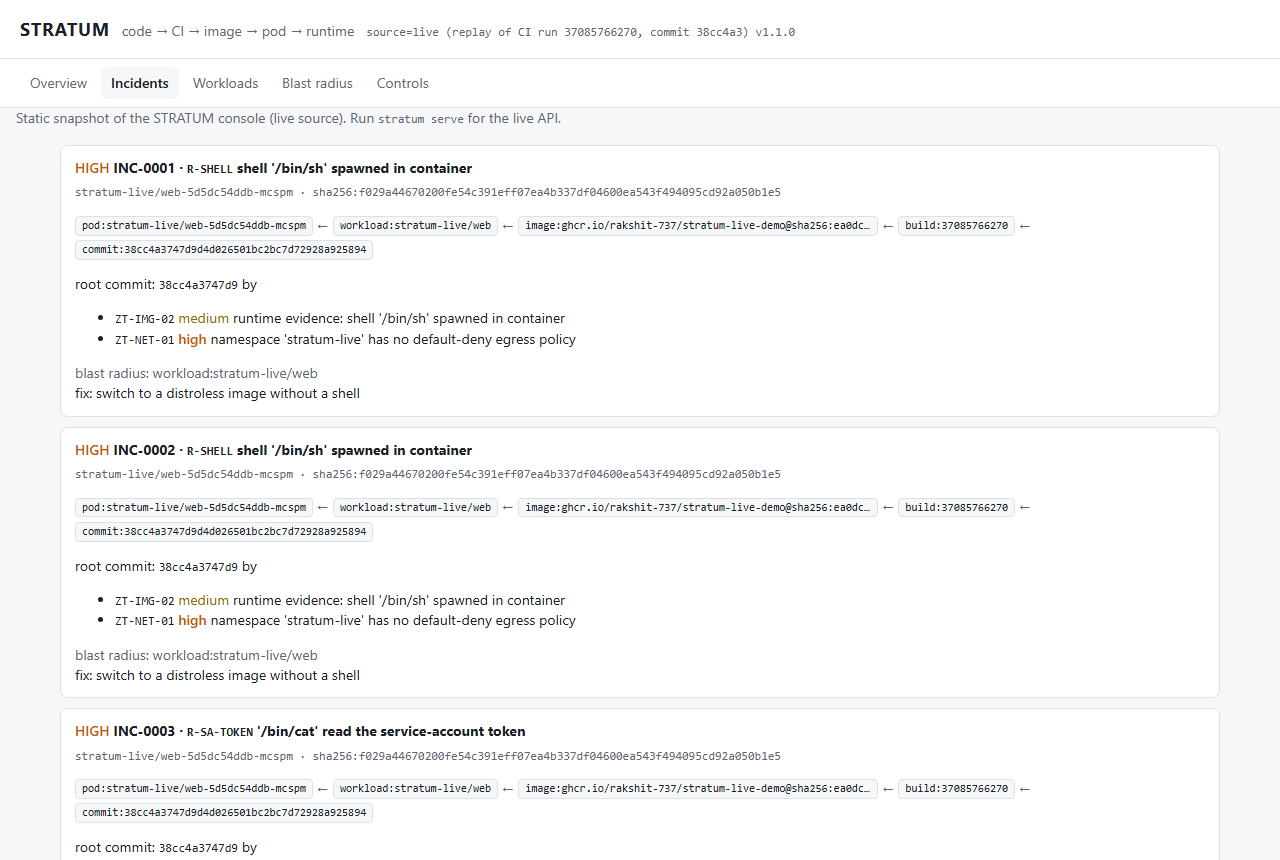
The console replaying job 1 of live run 37085766270 (commit 38cc4a3).
STRATUM is an open mini-CNAPP, not a Wiz. It puts commit → CI build → image → Kubernetes workload → pod →
runtime event into one graph and checks 13 Zero-Trust controls against it, in Python and mirrored in Rego
(also exported as a Gatekeeper ConstraintTemplate).
Headline results
| What | Result | Baseline or comparison |
|---|---|---|
| Live (CI): demo-pod alerts → commit read from each job's own Sigstore certificate | 5 / 5 runs fully traced (Wilson 95% CI 0.57-1.00), 55 / 55 incidents; 5 distinct certificates over 5 distinct digests (results/live.md, run 37085766270) |
1.0.0: commit injected by the workflow (circular); 1.1.0's published run: one certificate reused in 5 clusters, no run-level CI |
Live negative controls: unsigned upstream drift image; unsigned forged image with the right revision label |
0 / 5 and 0 / 5 incidents traced; ZT-PROV-01 named in 5 / 5 runs each (0.57-1.00) | label provenance (A2) and a repository join (A4) trace forged to the commit in 5 / 5 runs; A3 (STRATUM) in 0 / 5 |
| Live Gatekeeper and prevention | exported template denies the privileged pod 5 / 5; stratum prevent policy blocks the external sink and keeps in-cluster traffic 5 / 5 (each 0.57-1.00); 0 detections on the benign sink pod |
n/a |
| Policy engine vs upstream PSS conformance fixtures (148 pods, v1.37) | F1 1.000 at baseline and restricted (a conformance gate, deterministic) | v0.1 heuristic: recall 0.147 / 0.105 |
| Posture of 31 real projects in their default configuration | 32 / 87 workloads not PSS-restricted (7 privileged); 26 of 29 namespaces with no egress policy; 24 workloads with cluster-wide secret read or RBAC escalation (counts over the whole corpus) | v0.1 heuristic flags 7 / 87 |
| Rego mirror vs Python engine on the full corpus | 290 / 290 identical findings (OPA 1.21, results/opa.md) |
n/a |
| Trace pod → verified commit (86 real images, no runtime event) | 25 / 86 images (Wilson 0.21-0.39) carry a revision GitHub confirms; 23 / 87 workloads (0.18-0.37) from 11 / 31 projects (0.21-0.53) traced end to end | tag == git tag answers for 36 / 86 images (0.32-0.52) and agrees 21 / 21 where both answer; its other 15 answers cannot be verified |
| Runtime rules on real Tetragon events (30 events, 20 attack; in-sample, rules written on these events) | recall 0.80 [0.58, 0.92], precision 0.89 [0.67, 0.97]; 0 of 18 incidents reach a commit (no provenance on those images) | v0.1 rules: recall 0.40 [0.22, 0.61], precision 0.80 [0.49, 0.94] |
| Syscall model on ADFA-LD (4,372 normal / 746 attack), novelty n=5 | AUC 0.822 [0.803, 0.841]; TPR 0.082 [0.055, 0.133] at 1% FPR | split-dependent: STIDE n=6 ahead on the official split (0.827, paired +0.005 [0.002, 0.009], p ≈ 0.004); novelty n=5 ahead on 10 / 10 random re-splits (+0.023, corrected CI [0.001, 0.046], p ≈ 0.04) |
Container syscall traces (strace in Docker, 5 runs, leave-one-run-out), novelty n=5 |
AUC 0.826 (0.820-0.847 over runs; cluster bootstrap 0.67-0.94); separates 4 / 5 scripted action types (0.38-0.96) | STIDE n=6 is better: 0.900 (0.820-0.960); one action (cat of the token) is syscall-identical to a routine cat (run 37089906503) |
| Reproduction of Kim et al. 2016 (LSTM ensemble, ADFA-LD) | not reproduced: AUC 0.812 ± 0.005 over 3 seeds; every per-seed bootstrap CI (0.790-0.838) excludes 0.928 (run 37007358324, max 200 epochs) | paper: 0.928 |
| Trivy + CISA KEV on 49 real images | 10 critical / 156 high unique CVE × package pairs (15 / 432 summed per image); 0 KEV hits; Alpine 3.24.1 → 8-workload blast radius (counts) | n/a |
| Latency, full analysis of the real corpus (470 nodes, 504 edges) | median 21 ms (12-82 ms over 20 repeats) plus 4.8 s (4.7-5.4 s) to load the corpus, on a shared Windows laptop (results/perf.md) |
n/a |
Every number, with its method, source run and caveats, is on the Evaluation page; the Limitations page lists what is not shown.
Try it in 60 seconds
docker run --rm -p 127.0.0.1:8000:8000 ghcr.io/rakshit-737/stratum-cloud-security:latest # console on http://127.0.0.1:8000
The image is linux/amd64 only; on Apple silicon or other ARM hosts add --platform linux/amd64. Or:
git clone https://github.com/rakshit-737/stratum-cloud-security && cd stratum
pip install -e . && python -m stratum demo
Then: Getting started to check your own manifests, and Reproduce to regenerate every result.
Lab-only, defensive tool. It reads public manifests, registry metadata and published event logs, and it never changes a cluster. See Security.